
Vendor risk management
Vendor risk management
AuditIQ GRC is vendor risk management software for India. Assess vendors with questionnaires, track their documents and risk ratings, and keep evidence ready for DPDP processor duties and ISO supplier controls.
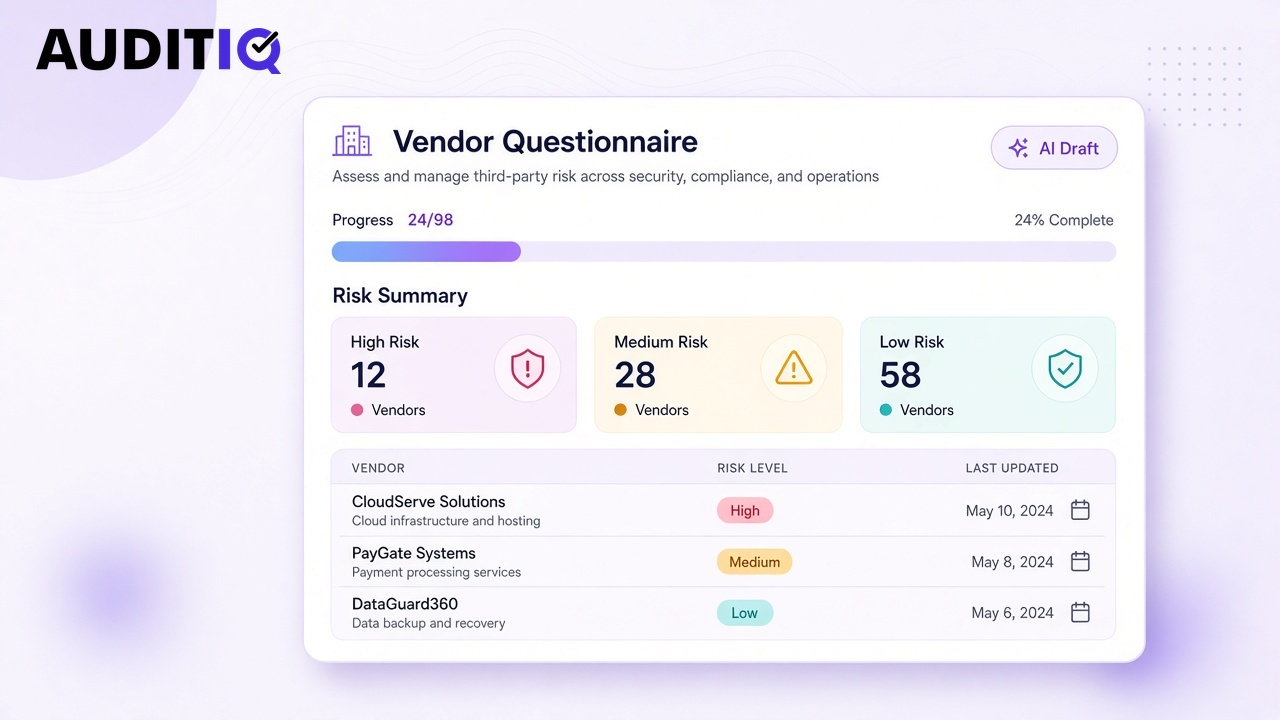
What does vendor risk management do?
Vendor inventory
Central register of suppliers, subprocessors and partners with data classification and business owner.
Basic Questionnaire
Lightweight vendor assessments for low-risk tools; deeper packs for processors holding personal data.
Document vault
DPAs, ISO certificates, SOC reports and contracts with expiry tracking in the shared Document Vault.
Inherent and residual risk
Score vendors consistently and record treatment plans when you accept residual risk.
Re-assessment cadence
Annual or event-driven reviews so audits do not surprise you with stale vendor evidence.
Sub-processor lists
Publish accurate processor lists to your trust center from the same inventory.
How vendor risk works
Inventory
List every vendor, what data they touch and who owns the relationship.
Assess
Send a questionnaire sized to the risk. Vendors answer through a secure link.
Rate
Score each vendor and record contracts, DPAs and certificates with expiry dates.
Monitor
Reminders before documents expire and re-assessments on a schedule.
Why does vendor risk matter under the DPDP Act?
Under the DPDP Act, a Data Fiduciary stays responsible for personal data its Data Processors handle, and may engage them only under a valid contract. Third party risk management software gives you the proof: who the processors are, what they signed and when they were last checked.
India use cases
Fintech and SaaS firms onboarding cloud processors, hospitals outsourcing diagnostics, manufacturers auditing logistics partners, and IT services firms maintaining client sub-processor lists for SOC 2 and DPDP together.
Connected modules
- Processor contracts satisfy DPDP and ISO supplier controls
- High-risk vendors open records in risk management
- Expired certificates trigger tasks before audits
- Onboarding checks align with supplier security policies
Moving off a spreadsheet? See GRC vs spreadsheets for vendor tracking pain points.
Vendor risk FAQ
Do vendors need an AuditIQ account?
No. Vendors answer questionnaires and upload documents through a secure link.
What is the Basic Questionnaire?
A lightweight assessment vendors (or internal teams) complete through a secure link, sized to risk, with templates for ISO, SOC 2 and DPDP or your own questions. See also organisation questionnaires.
Can we use our own questionnaire?
Yes. Use our templates for ISO 27001, SOC 2 and DPDP, or import your own.
How many vendors can we track?
There is no artificial cap. Mid-market customers routinely manage hundreds of tiered vendors in one register.
Can we import our existing vendor list?
Yes. CSV import during setup, including tier, owner and document expiry columns.
Do you store SOC 2 reports vendors share?
Yes. Reports sit on the vendor record with access limited to your team and optional NDA sharing via the trust center.
What if a vendor will not complete a questionnaire?
Record the refusal, escalate risk and document compensating controls, auditors ask for this trail.
Does this cover fourth parties?
Track sub-processors your vendors declare; deep fourth-party programmes may still need contractual flow-down clauses.
Make Trust Provable
See AuditIQ GRC run your frameworks
Book a 30-minute live demo. We map DPDP, ISO and SOC 2 onto one control set using your scope, not a slide deck.
- 30 minutes
- No obligation
- DPIIT Registered
- 50% off at launch