
Platform overview
One platform for compliance, risk and audits
AuditIQ GRC is a GRC platform built for Indian companies: from mapped policies and approval workflows to audit-ready proof in one place. AuditIQ GRC is based on these six frameworks and standards only: ISO 27001, ISO 27701, SOC 2, DPDP Act 2023, ISO 9001, ISO 42001. All six share one control library in the product. AI-assisted GRC across policies, evidence, risk, audits and security questionnaires. Controls, evidence, risks, audits, vendors, training, reports and Document Vault share one library so your team does the work once.
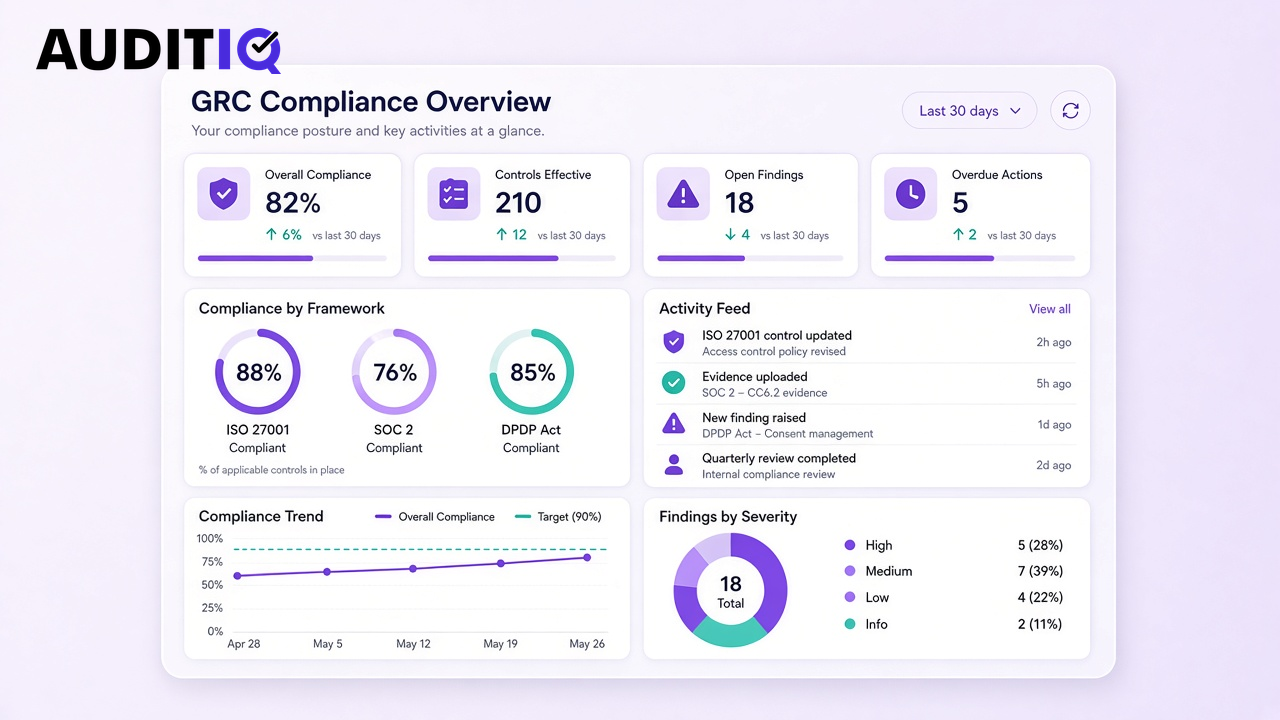
What is in the platform?
Eight core modules in the product menu share one control library and one evidence store, in the order shown on Inside AuditIQ.
Compliance frameworks
Admin completes the Basic Questionnaire; AuditIQ suggests frameworks and Master Admin can assign them manually.
ExploreGenerate policy
Creator drafts from the Policy Questionnaire; Reviewer and Approver workflow with change requests.
ExploreDMS Dashboard
Central view of policies, evidence and certificates in the Document Vault with version history.
ExploreTraining & Assessment
Assign training and assessments; track completion and results across the organisation.
ExploreRisk & Readiness (CRQ)
CRQ, Risk Genome and treatments to quantify risk and plan remediation.
ExploreTPRM
Vendor questionnaires, document collection and approve-or-improve decisions.
ExplorePlaybooks
Guided compliance workflows , module under active development in the product.
ExploreReports & Insights
Board-ready compliance status, gaps, policy progress and assessment summaries.
ExploreCapabilities already in the product
These modules ship with AuditIQ GRC today. Each is explained on its own page or under the parent module.
Business Units
Scope controls, risks and audits by entity, plant or business unit with clear owners.
OrganisationOrganizations & Users
Multi-entity workspaces, invites and roles for compliance, security and business owners.
Users & orgsPermission Setup
Fine-grained roles so auditors stay read-only and editors only see what they own.
PermissionsPolicy Calendar
Review, renew and acknowledgement deadlines on one calendar so policies never go stale.
See calendarDocument Vault
One secured library for policies, evidence and certificates with expiry and access control.
Document vaultRisk Quantification (CRQ)
Express risk in rupees and scenarios leadership can act on, not only heat-map colours.
See CRQRisk Genome
See how risks, controls, assets and frameworks connect so treatment work is not siloed.
See Risk GenomeRisk Treatments
Mitigate, transfer, avoid or accept with owners, tasks, target scores and review dates.
See treatmentsBasic Questionnaire
Lightweight assessments for vendors, staff or internal readiness without a full audit.
QuestionnairesTraining & Certifications
Awareness courses, assessments and certificates tied to the controls they support.
TrainingReports & Insights
Board, gap and trend views without rebuilding spreadsheets every quarter.
ReportsScreenshots of these modules are on Inside AuditIQ.
AI-assisted GRC
AI-assisted GRC across policies, evidence, risk, audits and security questionnaires
- Policy and control drafts from your approved library
- Evidence mapping and plain-language gap explanations
- Risk quantification (CRQ) and treatment suggestions
- Audit preparation and security questionnaire response drafts
- ISO 42001 impact assessment help for AI systems you build or use
Suggestions stay in your workspace until a human approves customer-facing content.
How does compliance automation work in AuditIQ GRC?
Four steps, the same for every framework.
Pick your frameworks
Turn on DPDP, ISO or SOC 2. AuditIQ GRC loads the controls, policies and evidence requests each one needs.
Map once
Shared controls are mapped across frameworks automatically. You see what you already meet.
Collect evidence
Assign owners, set due dates and upload or connect evidence. Reminders go out on their own.
Pass the audit
Give auditors read-only access, answer requests in one place and track findings to closure.
Who is AuditIQ GRC for?
Compliance, security and quality teams at Indian companies of every size: a startup preparing its first ISO 27001 audit, a mid-size firm adding DPDP to an existing ISMS, or a bank that needs everything on-premises.
- Startups and MSMEs running a first certification
- Mid-market companies running several frameworks
- Enterprises that need on-premises or their own cloud
Where does it run?
On AuditIQ cloud, in your own AWS, Azure or GCP account, or fully on-premises. The product is identical in all three, so you can start in the cloud and move later.
Why teams choose AuditIQ →Frameworks on the platform
ISO 27001
The global standard for an information security management system (ISMS).
Learn moreISO 27701
Extends ISO 27001 into privacy, and lines up closely with DPDP.
Learn moreSOC 2
Type 1 and Type 2 reports that US buyers ask for.
Learn moreDPDP Act 2023
India's personal data law: notice, consent, rights, breach reporting.
Learn moreISO 9001
Quality management, run together with ISO 27001.
Learn moreISO 42001
An AI management system for companies that build or use AI.
Learn moreTypical first projects on the platform
Most Indian teams do not turn on every module at once. They pick a certification or regulation, stand up controls and evidence, then add the rest as sales and regulators ask for more.
- DPDP readiness before May 2027, often alongside an existing ISMS
- First ISO 27001 for an enterprise deal or RBI-style security questionnaire
- SOC 2 Type II for US customers, mapped from ISO where possible
- ISO 9001 plus ISO 27001 for manufacturers who need both quality and security proof
Whichever path you take, the same control library and evidence store carry forward. Read how modules connect on Inside AuditIQ.
From spreadsheets to one source of truth
Many teams arrive with control matrices in Excel, risk registers in SharePoint and vendor lists in email. That works until a second framework arrives. AuditIQ GRC imports those registers, links each row to live control status and stops you collecting the same screenshot three times for three audits.
See an honest side-by-side in GRC software vs spreadsheets, then browse screens in Inside AuditIQ.
Questions about the platform
Is AuditIQ GRC compliance automation software?
Yes. It automates the repetitive parts of compliance: mapping controls across frameworks, requesting and reminding for evidence, tracking policy sign-offs and following up audit findings. People still make the decisions; the platform does the chasing.
Can we start with one module?
Yes. Most teams start with compliance management for one framework, then add risk, vendor or audit management as they grow. Everything stays connected.
Can we import our existing spreadsheets?
Yes. Controls, risks, assets and vendors can be imported from Excel or CSV during setup, and our team helps with the first import.
Does every module cost extra?
Pricing is based on your deployment size and frameworks, not a separate licence per module. In a demo we show which modules you need on day one and which can wait.
Can auditors use the platform without editing our data?
Yes. Audit management gives certification bodies and internal auditors read-only access to the evidence in scope. Auditor seats do not count as full users.
Make Trust Provable
See AuditIQ GRC run your frameworks
Book a 30-minute live demo. We map DPDP, ISO and SOC 2 onto one control set using your scope, not a slide deck.
- 30 minutes
- No obligation
- DPIIT Registered
- 50% off at launch