
Compliance management
Compliance management
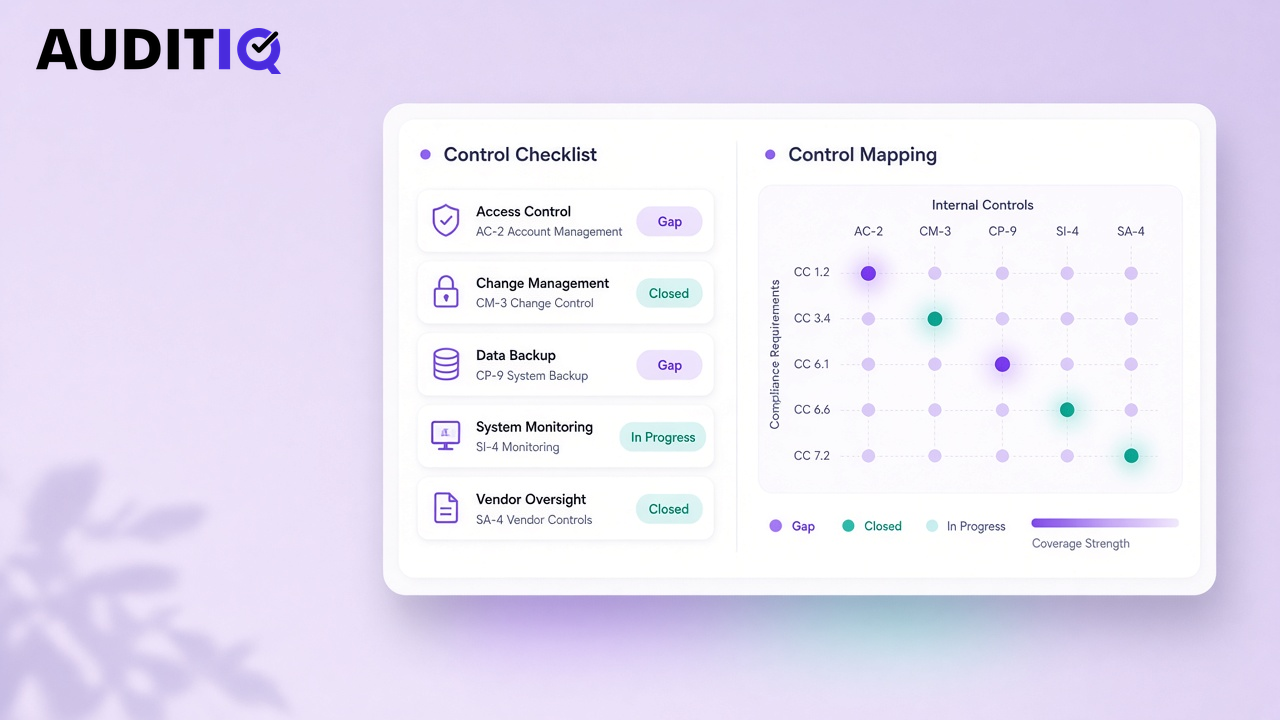
AuditIQ GRC is compliance management software for India. It keeps your controls, evidence and gaps for DPDP, ISO and SOC 2 in one place, and maps each control once to every framework that needs it.
What does it do?
One control library
Pre-built controls for all six frameworks, mapped to each other. Edit once, updated everywhere.
Gap view per framework
See exactly which requirements are met, partly met or missing, and who owns each fix.
Evidence that counts twice
Every file or connected check counts for every control and framework it supports.
Owners and reminders
Assign controls to people, set review dates and let the platform do the chasing.
Statement of Applicability
Generate your ISO 27001 SoA from live control status, not a stale spreadsheet.
Board-ready reporting
Readiness by framework, entity and owner, exported as PDF or Excel.
How compliance management works
Turn on frameworks
Select DPDP, ISO or SOC 2. The platform loads requirements and maps them to the shared control library.
Scope and assign
Mark controls in or out of scope for each entity. Assign owners and review cadences so nothing sits unowned.
Close gaps
Gap view shows what is missing per framework. Tasks, policies and evidence requests link directly from each row.
Report readiness
Export readiness by framework for leadership, customers or your certification body.
India use cases
Compliance management is usually the first module teams turn on, often when a customer security questionnaire, DPDP deadline or bank vendor assessment lands on the desk.
- IT exporters adding SOC 2 without rebuilding ISO 27001 work
- DPDP gap analysis before May 2027, mapped to existing Annex A controls
- Group companies with separate entities but shared IT policies
- Quality-led manufacturers extending ISO 9001 scope to information security
Connected modules
Control status drives the risk register. Policies in policy management satisfy control rows automatically when published. Evidence from integrations flips controls green. Audits sample from the same library. High-level status can surface on your trust center when you choose to publish it.
How is this different from control management in a spreadsheet?
A spreadsheet tells you what the control is. Control management software tells you whether it is working today, who owns it, where the evidence is and which frameworks fail if it breaks. When you add a second framework, you do not start a second spreadsheet. Read GRC software vs spreadsheets.
Compliance management FAQ
Which frameworks does compliance management cover?
DPDP Act 2023, ISO 27001, ISO 27701, ISO 42001, ISO 9001 and SOC 2, all on one shared control set. Custom internal controls can be added too.
Can we use our own control wording?
Yes. Start from our library and rewrite controls in your own words; the framework mappings stay intact.
Does it handle multiple entities?
Yes. Group companies can track each entity separately and share common controls across them.
Can we track RBI, SEBI or IRDAI expectations?
Yes. Native RBI, SEBI and IRDAI packs are planned to launch together. Today, teams map sector circulars as custom controls beside ISO 27001 and DPDP. See the India regulators hub.
How does mapping save time?
When you enable a second framework, the platform shows overlap immediately, often 60-80% for SOC 2 and ISO 27001, so you only implement net-new controls.
Does it generate ISO 27001 Statement of Applicability?
Yes. SoA exports from live scope decisions and control status, not a static Word file from last year.
Can consultants work inside our tenant?
Yes. Consultant roles are read-write on agreed modules without seeing unrelated entities.
Make Trust Provable
See AuditIQ GRC run your frameworks
Book a 30-minute live demo. We map DPDP, ISO and SOC 2 onto one control set using your scope, not a slide deck.
- 30 minutes
- No obligation
- DPIIT Registered
- 50% off at launch