
Audit management
Audit management
AuditIQ GRC is audit management software for India. Plan internal and certification audits, share evidence with auditors in one workspace and track every finding to closure, for ISO, SOC 2 and DPDP.
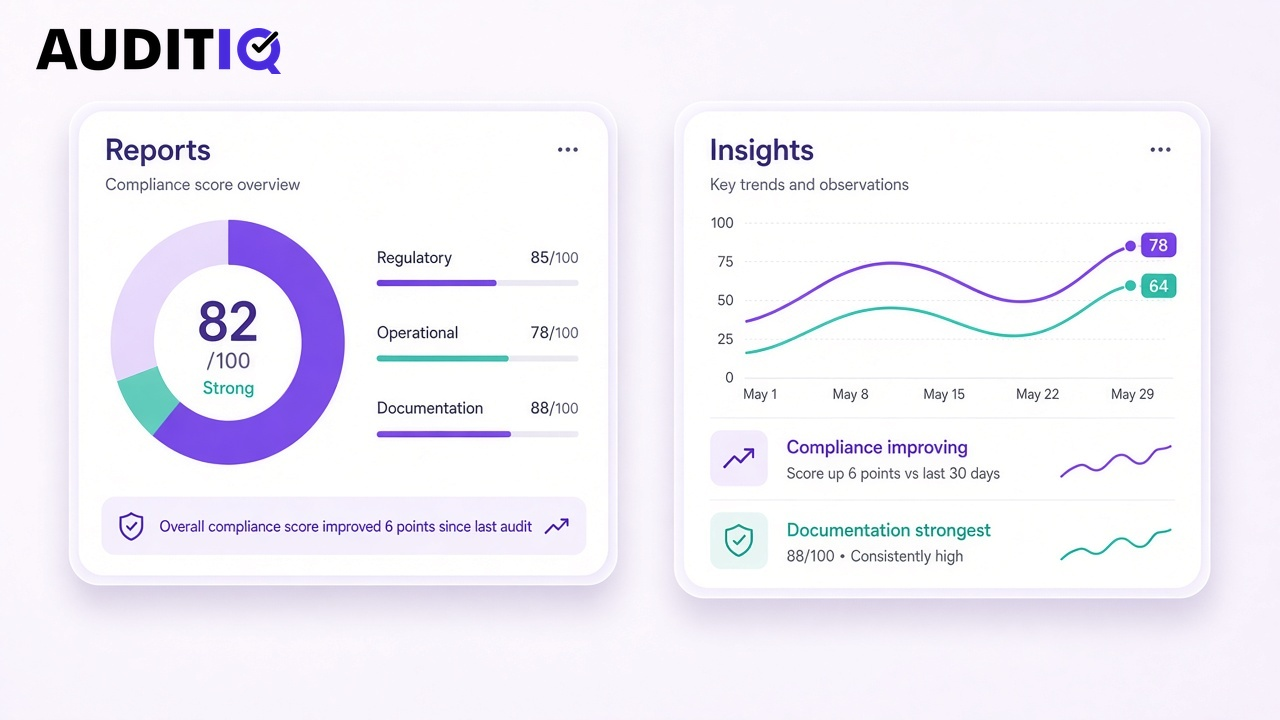
What does audit management do?
Audit calendar
Internal audits, surveillance audits and recertifications for every framework on one calendar.
Auditor workspace
Read-only access to the evidence in scope. Requests and replies in one thread, not fifty emails.
Findings and CAPA
Log non-conformities, assign corrective actions and prove closure at the next audit.
Checklists
Clause-based internal audit checklists for ISO and themed reviews for DPDP duties.
Sampling notes
Record what you sampled and why, so external auditors trust your internal programme.
SOC 2 period support
Track examination period evidence requests alongside ISO surveillance visits.
How audit management works
Plan
Schedule internal and external audits per framework and entity on one calendar.
Scope
Select controls and evidence packages to share; everything else stays hidden.
Execute
Auditors request clarifications in-thread; owners respond without email chains.
Close
Findings become CAPA tasks with due dates; closure evidence is visible at the next visit.
Does it support internal audits for ISO 27001 and ISO 9001?
Yes. Both standards require a planned internal audit programme (clause 9.2). AuditIQ GRC gives you audit plans, checklists per clause, sampling notes and a findings log, and because ISO 9001 and ISO 27001 share clause structure, you can audit both in one cycle. Read running ISO 9001 and ISO 27001 together.
India use cases and connections
- Stage 1 and Stage 2 ISO audits with Indian certification bodies
- DPDP readiness reviews before Board or leadership sign-off
- Customer-conducted audits of SaaS vendors using read-only workspaces
- Evidence pulled from compliance management and integrations
- Findings that raise risks or require policy updates
Audit management FAQ
Do auditors need to pay for access?
No. Auditor seats are free and read-only, limited to the audit you share.
Can we choose our own certification body?
Yes. AuditIQ GRC works with any accredited certification body or CPA firm. We do not require a specific auditor.
Can external auditors upload their report?
Yes. Store the certificate and audit report against the audit record for surveillance planning.
Does it support SOC 2 Type II?
Yes. Track the examination period, customer requests and bridge letters alongside ISO workpapers.
How do we prove CAPA closure?
Each finding links to tasks and re-test evidence. Auditors see the full thread at the next audit.
Can we run audits offline at a plant?
On-premises deployments keep audit data inside your network; export packs when you need paper binders.
Make Trust Provable
See AuditIQ GRC run your frameworks
Book a 30-minute live demo. We map DPDP, ISO and SOC 2 onto one control set using your scope, not a slide deck.
- 30 minutes
- No obligation
- DPIIT Registered
- 50% off at launch