
Inside AuditIQ
See AuditIQ modules in branded mockups
Eight core modules in the same order as the product menu, branded marketing mockups that show the shape of each module without exposing live product screens.
1 · Compliance frameworks
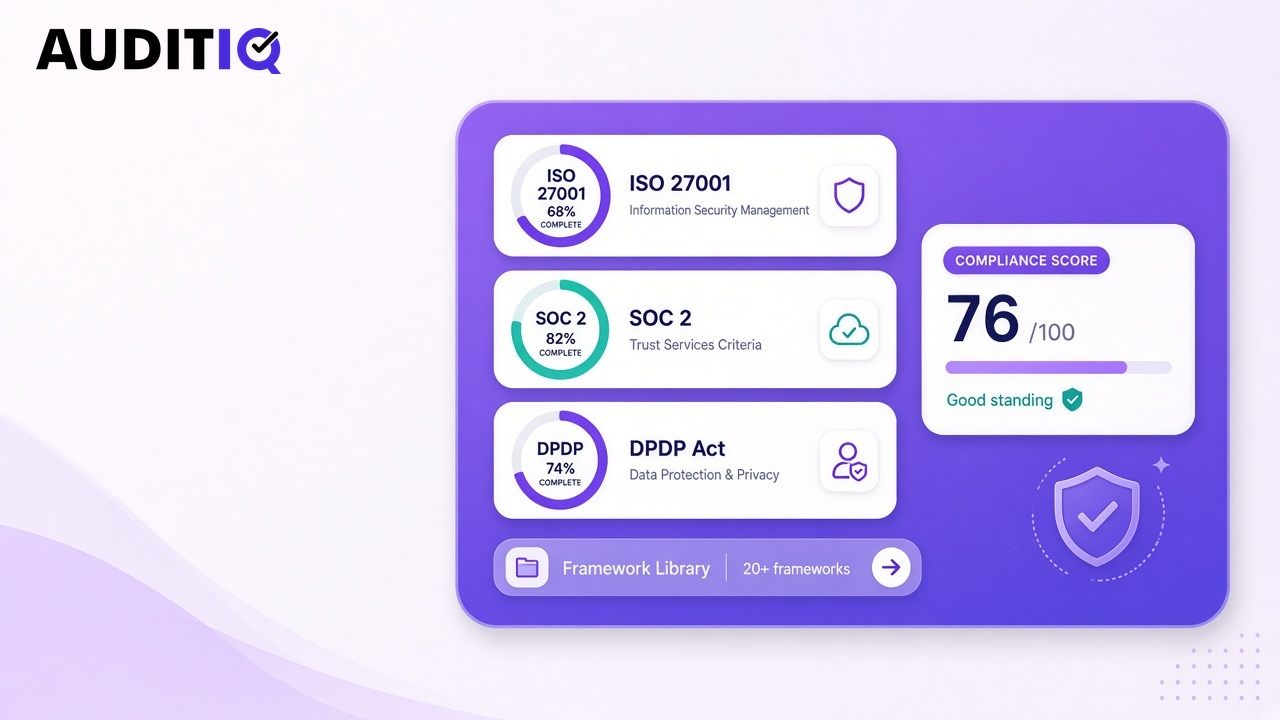
Compliance Framework
Compliance Framework Management: Admin completes the Basic Questionnaire with organization details and business requirements. AuditIQ identifies and generates the relevant compliance frameworks based on the organization's needs, while the Master Admin can also manually assign specific compliance frameworks to the organization.
2 · Generate policy
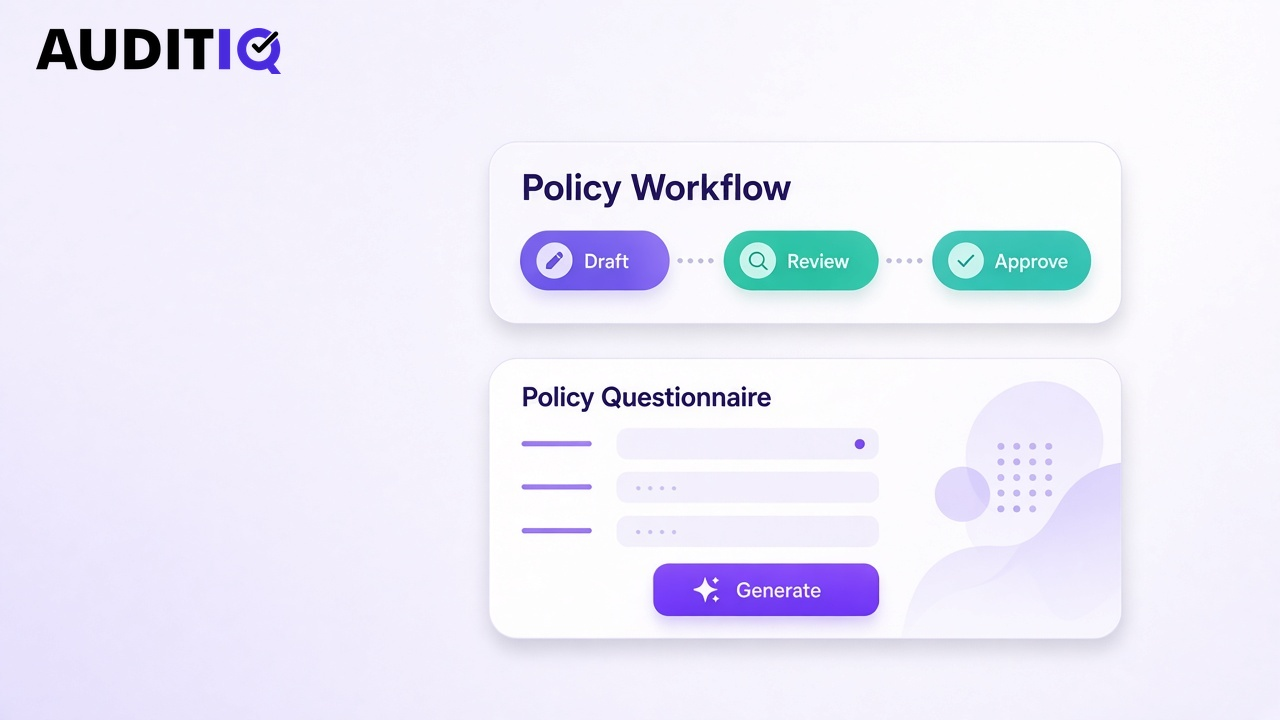
Generate Policy
Policy Generation : The Creator completes the Policy Questionnaire and generates the policy in Draft status. The Reviewer reviews it, followed by the Approver for final approval. If changes are required, the policy is sent back to the Creator through a Change Request. The Creator makes the necessary changes, and the policy goes through the Reviewer and Approver workflow again.
3 · DMS Dashboard
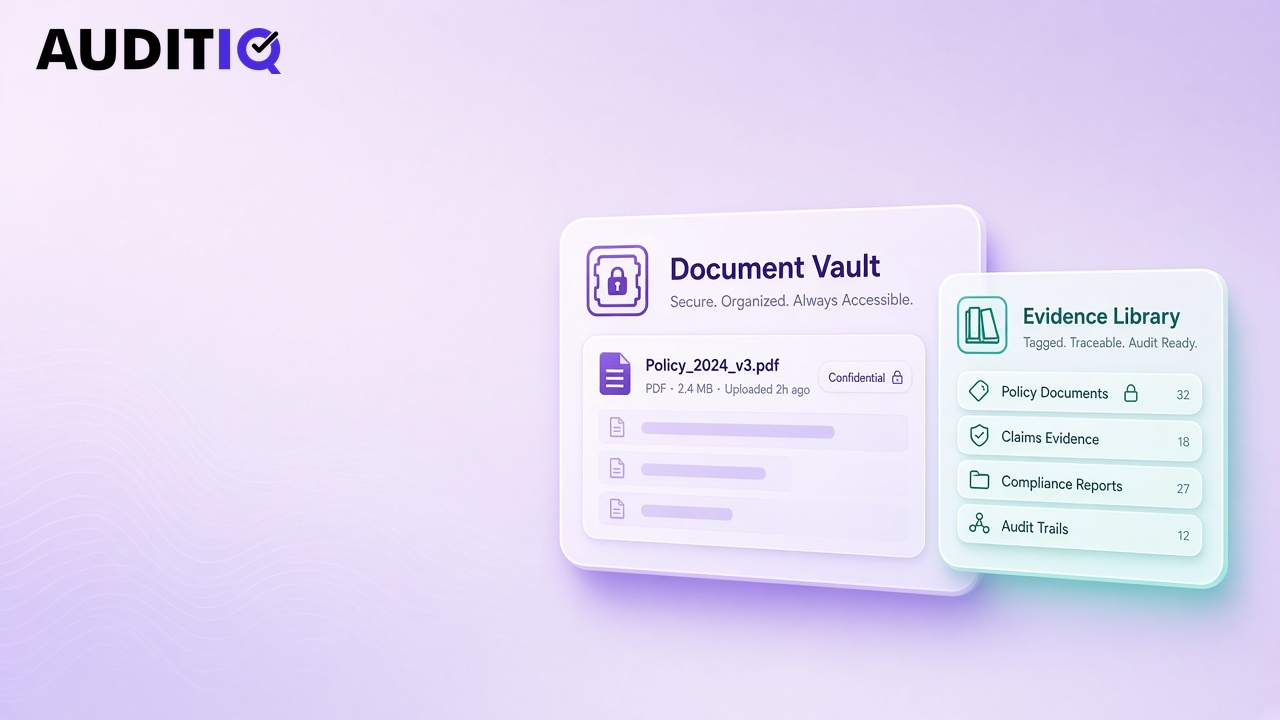
DMS Dashboard
Document Management System (DMS) : The DMS Dashboard provides a centralized view of all organizational documents, policies, and supporting evidence stored in the Document Vault. It allows users to upload, access, organize, and manage documents while maintaining version history and document security.
4 · Training & Assessment
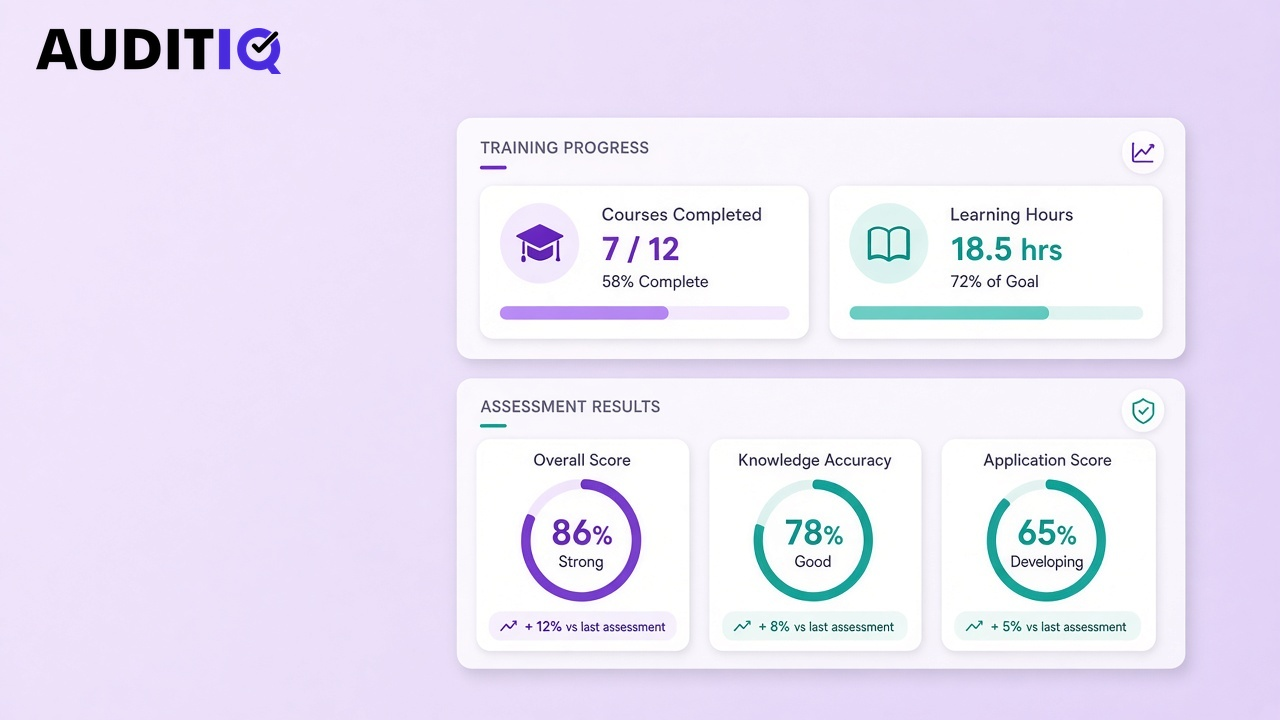
Training & Assessment
Training & Assessment: This module helps organizations educate employees about security policies, compliance requirements, and organizational practices. Employees complete assigned training and assessments to evaluate their understanding. Admins can monitor training progress, assessment results, and employee completion status.
5 · Risk & Readiness (CRQ)
Risk & Readiness CRQ
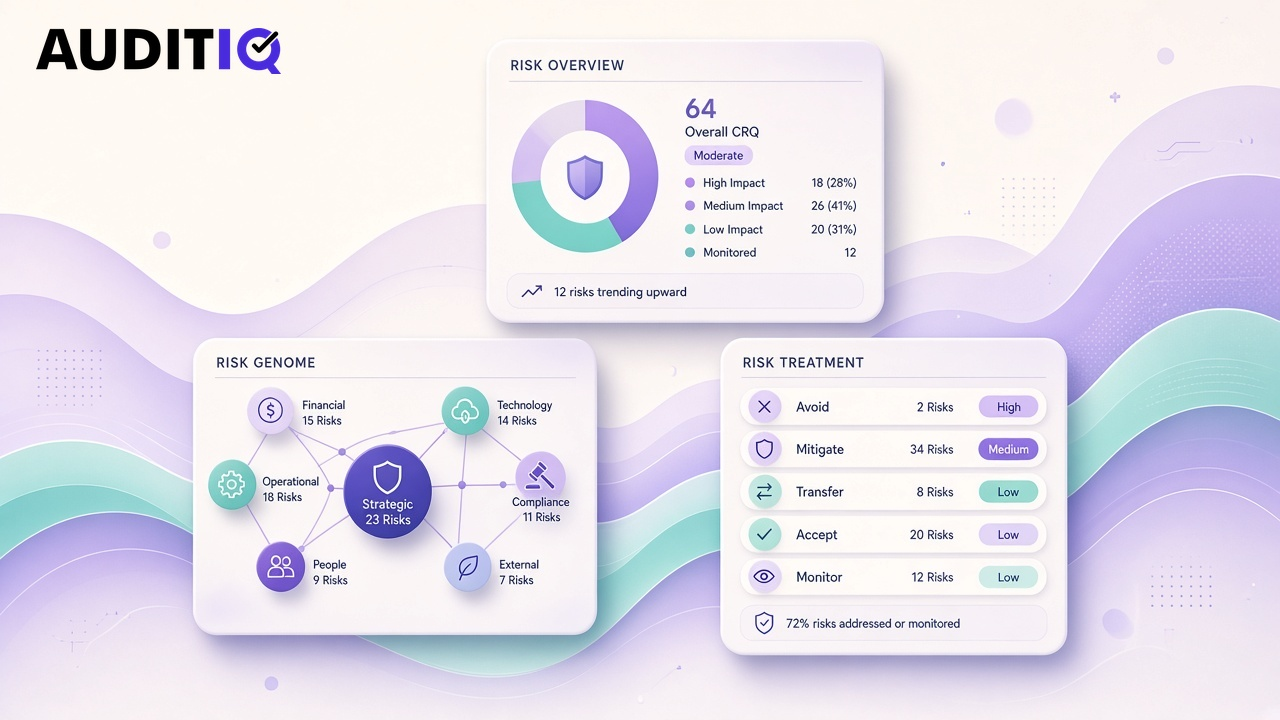
Risk & Readiness (CRQ): Helps organizations identify and understand potential risks, measure their impact on the business, and estimate possible financial losses. It also helps users decide how to reduce or fix risks through Risk Treatment and understand connected risk patterns through Risk Genome.
6 · TPRM
TPRM
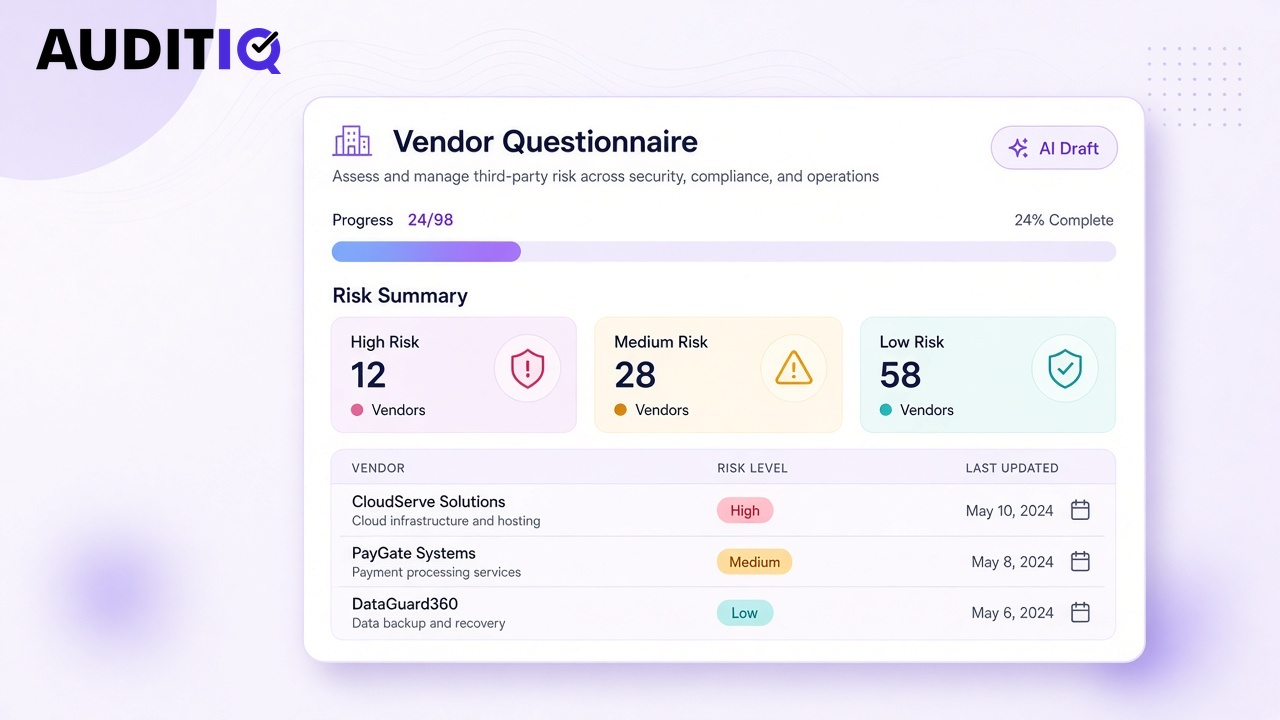
Third-Party Risk Management (TPRM): The organization adds its vendors or third-party service providers and sends them security and compliance questionnaires. Vendors submit their responses and supporting documents, which are reviewed to identify potential risks. Based on the assessment, the organization evaluates vendor risk and decides whether to approve the vendor or request improvements.
7 · Playbooks
Playbooks
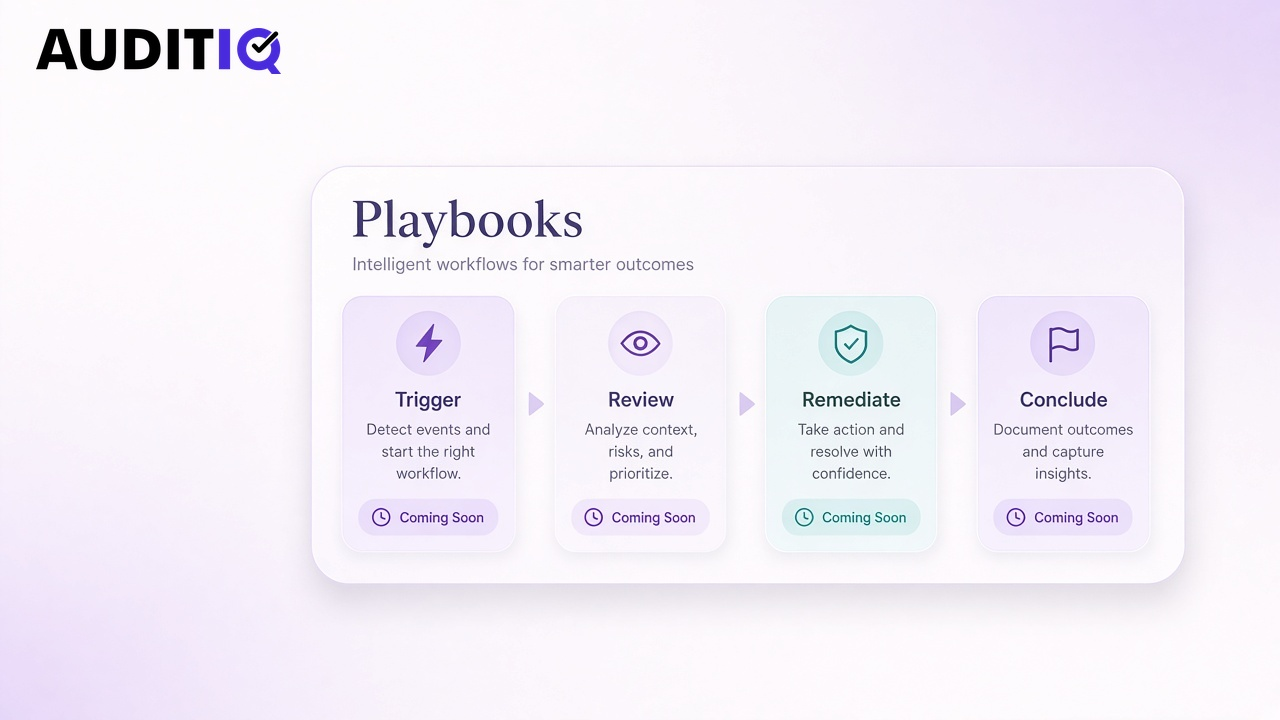
Playbooks: Playbooks are under development. Stay tuned for smarter workflows and simplified compliance management Coming soon
8 · Reports & Insights
Report & Insights
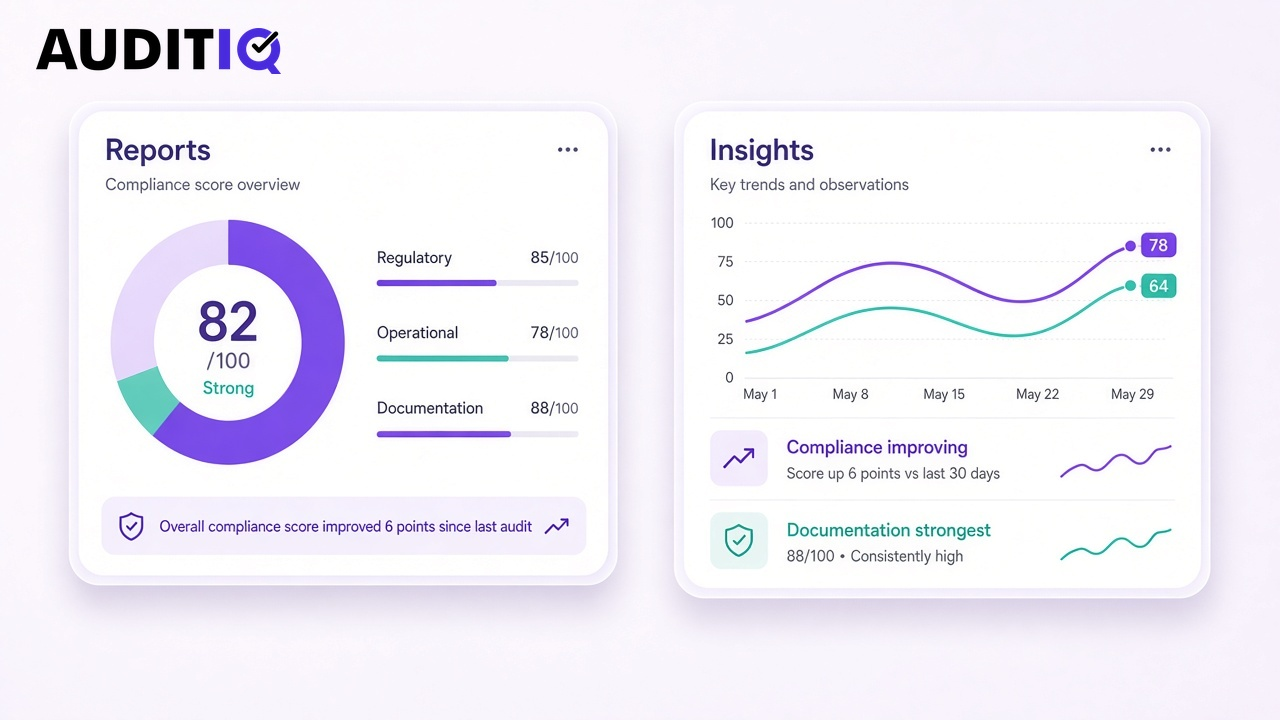
Reports & Insights: This module provides a centralized view of the organization's compliance status, risk levels, policy progress, and assessment results. Users can generate reports, track completed and pending activities, identify compliance gaps, and understand overall organizational security and compliance performance.
See it on your scope
Book a demo to walk through these modules with your frameworks and entities loaded, or explore the full platform overview.
Make Trust Provable
See AuditIQ GRC run your frameworks
Book a 30-minute live demo. We map DPDP, ISO and SOC 2 onto one control set using your scope, not a slide deck.
- 30 minutes
- No obligation
- DPIIT Registered
- 50% off at launch