
Trust center
Trust center
AuditIQ GRC includes trust center software: publish a branded page with your certifications, policies and security posture, and share sensitive documents like SOC 2 reports with buyers under NDA.
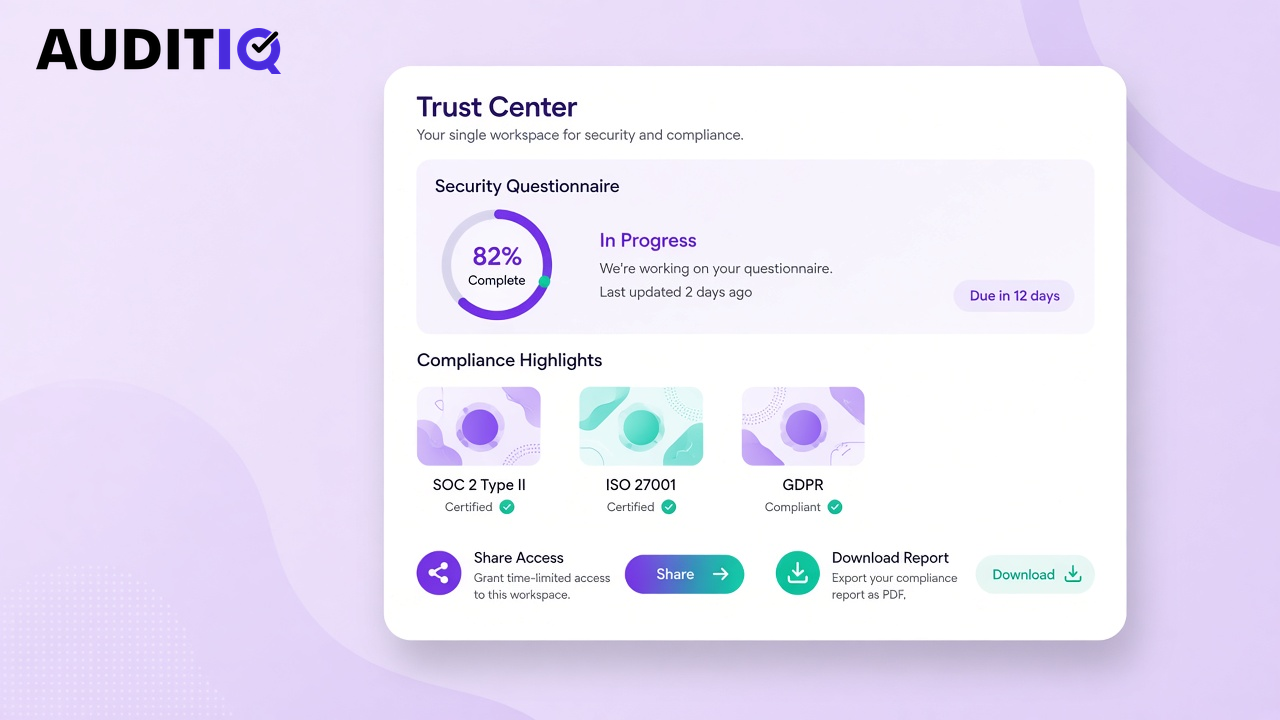
What does the trust center do?
Always current
Certificates and control status come straight from your compliance workspace, no duplicate CMS updates after every audit.
NDA-gated documents
Buyers request access, accept your NDA online and download reports with a watermark.
Faster security reviews
Point prospects to one link instead of filling in the same questionnaire again.
Public policy library
Publish privacy, security and AI policies pulled from policy management.
Sub-processor transparency
Show subprocessors from your vendor inventory with last review dates.
Custom branding
Your logo, colours and domain path, not a generic third-party badge page.
How the trust center works
Choose what to publish
Pick certifications, policies, FAQs and sub-processor lists you are comfortable showing publicly.
Gate sensitive files
SOC 2 reports, penetration test summaries and DPAs sit behind NDA and approval workflow.
Sync from GRC work
When control status or certificates change in compliance management, the trust center reflects it.
Track requests
See who asked for gated documents, when they signed the NDA and what they downloaded.
What is a security trust portal?
A security trust portal is a public page that shows customers how you protect their data: certifications, policies, sub-processors and security practices. It shortens enterprise sales cycles because buyers can self-serve the answers they need.
Who needs it in India
B2B SaaS selling to Indian enterprises and banks, IT services firms answering offshore client security teams, fintechs in due diligence with NBFC partners, and any company that wins deals faster when procurement can verify ISO or SOC 2 without a week of email.
You can publish while still working towards certification, honestly show programme status, not fake badges. That is how many startups keep enterprise conversations warm.
Connected modules
- Certificates and gap summaries from compliance management
- Policies and acknowledgement status from policy management
- Vendor and sub-processor data from vendor risk
- Audit reports filed through audit management
- Evidence collection continues in integrations, the trust center is the shop window, not the warehouse
Want to see how buyers experience it? Browse Inside AuditIQ or book a demo.
Trust center vs emailing PDFs
Emailing the same SOC 2 report to fifty prospects creates version drift and no audit trail. A trust center gives each buyer a current link, logs NDA acceptance and lets you revoke access when a report ages out. It does not replace due diligence on high-risk deals, it removes repetitive work on the long tail of security questionnaires.
Trust center FAQ
Can we use our own domain?
Yes. Host the trust center on a subdomain you control, such as trust.yourcompany.com.
Will it show failed controls to the public?
You choose what is public. Most teams show certifications and policies publicly, and keep detailed gap views internal.
Does every viewer need an NDA?
Only for documents you mark gated. Public policies and certification badges need no login.
Can we answer SIG or CAIQ from here?
The trust center reduces repeat questions; lengthy bespoke questionnaires may still need a dedicated response. Many teams pair it with evidence exports from compliance management.
Is the trust center a separate product?
No. It is included with AuditIQ GRC and reads from the same data as your GRC modules.
Can we publish DPDP-specific notices?
Yes. Link privacy notices and grievance contacts required under the DPDP Act.
What about customers who insist on their own portal?
Export the same artefacts to their vendor system; your trust center remains the source you control.
Make Trust Provable
See AuditIQ GRC run your frameworks
Book a 30-minute live demo. We map DPDP, ISO and SOC 2 onto one control set using your scope, not a slide deck.
- 30 minutes
- No obligation
- DPIIT Registered
- 50% off at launch