
Policy management
Policy management
AuditIQ GRC is policy management software that lets you draft, approve and publish policies from ready templates, track acknowledgements on a Policy Calendar, and map every policy to the controls it supports.
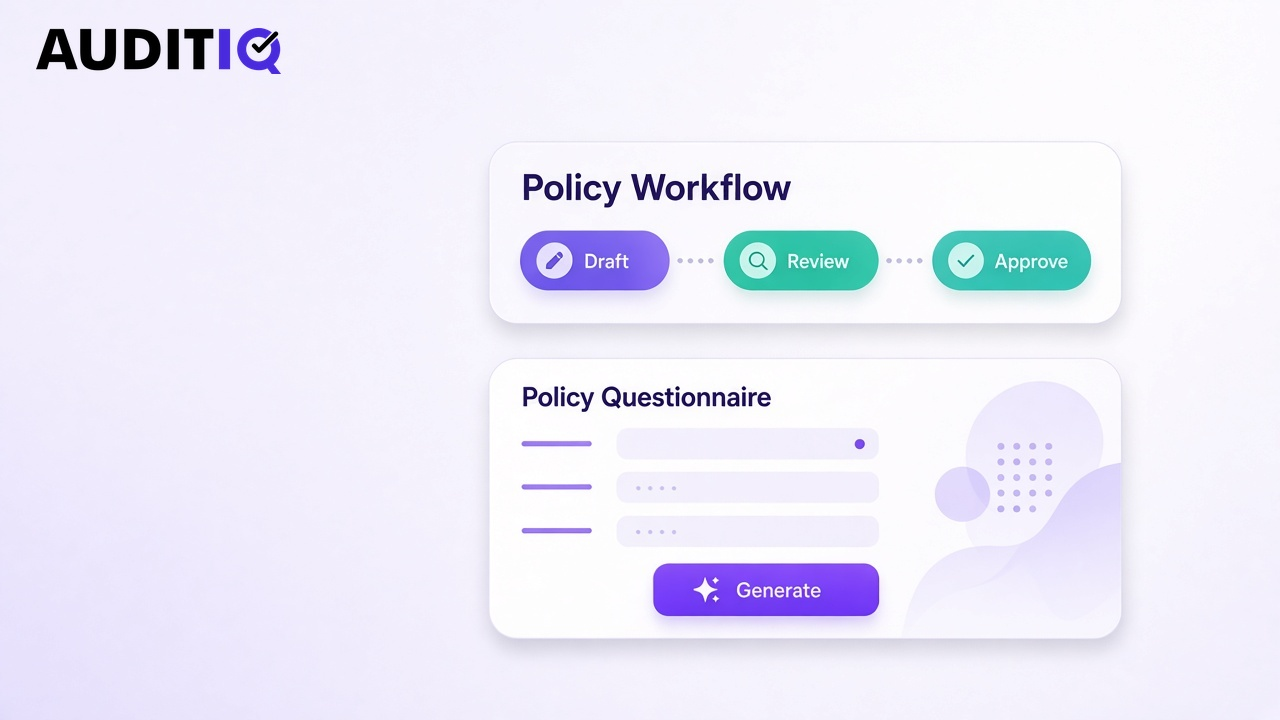
What does policy management do?
Ready templates
ISO 27001 policy templates plus DPDP privacy notice, retention, breach response and AI use policies, written in plain English.
Approvals and versions
Review, approve and publish with a full version history auditors can follow.
Policy Calendar
Review, renew and acknowledgement deadlines in one calendar so nothing slips past surveillance.
Acknowledgements
Send policies to staff, track who has read and accepted them, and remind the rest.
Control mapping
Each published policy satisfies mapped rows in compliance management automatically.
Customer-facing copies
Publish selected policies to your trust center without duplicate uploads.
Policy Calendar
A living calendar of policy reviews, renewals and acknowledgement campaigns, not a sticky note before the next audit.
Review dates
See which policies are due for annual or triggered review across business units.
Acknowledgement windows
Plan campaigns for new joiners, contractors and yearly re-attestation.
Audit evidence
Export calendar outcomes and sign-off logs when certification bodies ask for proof of currency.
Pair the calendar with Training & Certifications when a policy requires a course, not only a signature.
How policy management works
Draft or import
Start from a template or upload existing Word and PDF files.
Review and approve
Route through legal, CISO or management with comments captured per version.
Publish and map
Link the policy to controls so gap status updates when it goes live.
Acknowledge and renew
Staff sign off electronically; annual review reminders keep policies from going stale.
Which policies does ISO 27001 need?
ISO 27001 requires an information security policy and topic-specific policies that support your Annex A controls, such as access control, acceptable use and supplier security. DPDP adds privacy notices, retention and breach response. AuditIQ GRC includes templates for each and links them to the right controls, so a policy review also updates your compliance status.
India use cases
- First-time ISMS teams replacing scattered Google Docs before certification
- DPDP privacy notices and breach playbooks aligned with MeitY rules
- ISO 9001 document control sharing procedures with the security policy set
- Remote-first companies proving annual acceptable-use training to SOC 2 auditors
See also free templates and the Inside AuditIQ evidence chapter.
Policy management FAQ
Can we upload our existing policies?
Yes. Upload Word or PDF policies and map them to controls. You do not have to rewrite anything to get started.
Do employees need a licence to acknowledge policies?
No. Staff acknowledge through a simple link or your SSO; they do not need a full user licence.
Can we run policies in Hindi or regional languages?
Yes. Publish multiple language versions; acknowledgements track per language where you require them.
How do auditors verify staff read policies?
Export acknowledgement logs with timestamps and policy version numbers.
What is the Policy Calendar?
It is the schedule of policy reviews, renewals and acknowledgement campaigns so owners know what is due before an auditor asks.
Does policy review update ISO management review records?
Review dates and outcomes feed compliance reporting you can cite in management review packs.
Can contractors acknowledge policies?
Yes. Invite contractors by email the same way as employees; they do not consume full seats.
Make Trust Provable
See AuditIQ GRC run your frameworks
Book a 30-minute live demo. We map DPDP, ISO and SOC 2 onto one control set using your scope, not a slide deck.
- 30 minutes
- No obligation
- DPIIT Registered
- 50% off at launch