
Make Trust Provable
Unified GRC Platform for DPDP, ISO 27001 and SOC 2 Compliance in India
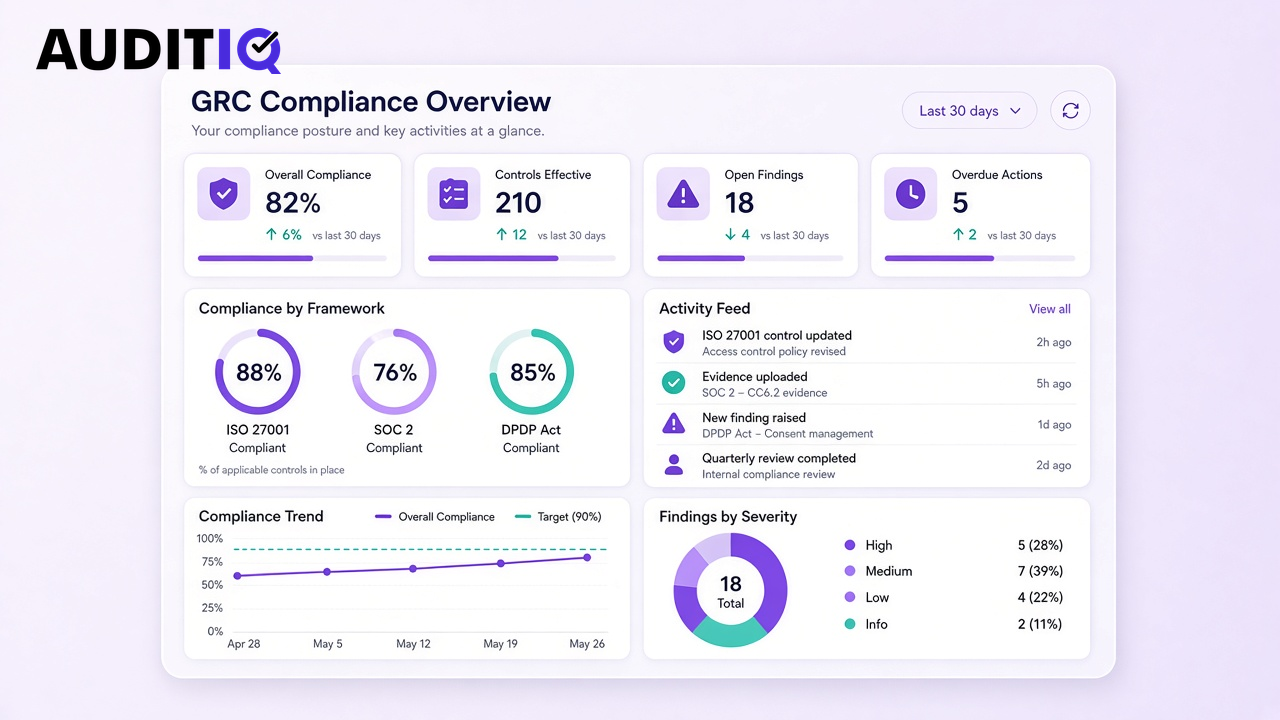
Map each control once, centralise your compliance evidence, and reuse it across DPDP Act 2023, ISO 27001, ISO 27701, ISO 42001, ISO 9001 and SOC 2, from policies and approvals to proof auditors can verify. AI-assisted GRC across policies, evidence, risk, audits and security questionnaires. Stay audit-ready on AuditIQ cloud, your own cloud or fully on-premises.
-
One-time control mapping
Map a control once and it covers every framework that needs it.
-
Centralised compliance evidence
All policies, records and audit evidence in one place, not scattered across drives.
-
Evidence reuse across frameworks
Collect evidence once and reuse it for DPDP, ISO and SOC 2 audits.
- 6Frameworks on one control set
- 3Deploy options: cloud, your cloud, on-prem
- DPIITRegistered Indian startup
- AIAssisted GRC built into the platform
- 50% offLaunch pricing for India
At a glance
What is AuditIQ?
AuditIQ is a unified GRC (governance, risk and compliance) platform built in India. It brings controls, evidence, risks, policies, audits and vendors into one system of record, with AI-assisted GRC across policies, evidence, risk, audits and security questionnaires, so Indian compliance teams can get certified and stay audit-ready for DPDP, ISO and SOC 2, whether it’s their first certification or several running at once.
Organisation & scope
Business units, users and permissions before you map controls
Control & evidence
One shared library; collect once, reuse everywhere
Policies & vault
Policy Calendar plus Document Vault for evidence
Risk, CRQ & treatments
Risk Genome, quantification and treatment plans
Audits & vendors
Certification audits, processor questionnaires and evidence
Training, reports & trust
Awareness, board packs and your buyer Trust Center
-
6
Frameworks on one control set
DPDP Act 2023, ISO 27001, ISO 27701, ISO 42001, ISO 9001 and SOC 2, mapped to one shared control library, so each new framework builds on work you’ve already done.
-
1
Evidence library, reused everywhere
Collect a piece of evidence once and it counts toward every framework and audit it applies to, automatically.
-
3
Ways to deploy
AuditIQ cloud, your own cloud account, or fully on-premises. Same platform, your choice of infrastructure and data residency.
Why AuditIQ
Why teams choose AuditIQ GRC
Comply once, stay audit-ready, and prove trust, built for Indian rules and priced for Indian companies.
- 01
Comply once, certify many
Map a control once and reuse it across six frameworks. Your team doesn’t redo work.
- 02
DPDP-ready from day one
India’s data protection law is built in from the start, not added later to a global tool.
- 03
Audit in weeks, not months
Guided workflows, evidence tracking and gap reports keep you continuously audit-ready.
- 04
AI-assisted GRC built in
AI-assisted GRC across policies, evidence, risk, audits and security questionnaires. ISO 42001 maps how you govern AI products on the same control library.
- 05
Built by practitioners
Designed by a team that runs real ISO and VAPT audits, so it follows how auditors actually work.
- 06
Priced for India
Enterprise-grade GRC at a fraction of global tool costs, with 50% off at launch.
Partners & recognition
Trusted partners
Technology and training partners, with DPIIT startup recognition.
 Microsoft AzureCloud partner
 Cyber Octet Pvt LtdCybersecurity & GRC partner
 School of Cyber SecurityTraining partner
 DPIIT RegisteredStartup recognition
Get started
Where are you starting your compliance journey?
Getting ISO 27001 certified for the first time, adding DPDP compliance to an existing ISMS, or managing several frameworks at once: pick your path. The platform underneath is the same, so you never switch tools as you grow.
-
01Startups & MSMEs
Your first ISO 27001, SOC 2 or DPDP programme
Go from zero to audit-ready without hiring a full compliance team.
- Ready-made policy and control templates
- Guided scoping and a step-by-step implementation path
- Clear view of what’s left before your certification audit
-
02ISO 27001-certified teams
Already ISO 27001 certified, now adding DPDP
Reuse the ISO 27001 controls you already have, add the DPDP-specific obligations, and keep one evidence set for both.
- See which existing controls already cover DPDP
- Add what’s new: consent, notices, data principal rights and breach reporting
- Get ready ahead of the 13 May 2027 DPDP deadline
-
03Growing & enterprise teams
Managing multiple compliance frameworks
Consolidate DPDP, ISO and SOC 2 programmes run in spreadsheets or point tools into one GRC platform.
- One control set across all six frameworks
- One risk register and one audit calendar
- One evidence library, no duplicate audit requests
Not sure which path fits? Book a demo and we’ll map it with you.
How it works
From first framework to audit-ready in four steps
Pick frameworks, map controls once, collect evidence, then share a clean pack with auditors. Built around DPDP, ISO and SOC 2 for Indian teams.
Pick your frameworks
Turn on DPDP, ISO 27001, ISO 27701, ISO 42001, ISO 9001 or SOC 2. AuditIQ loads the controls, policies and evidence each one needs.
Map once
Shared controls map across frameworks automatically. You see what you already meet before you collect anything new.
Collect evidence
Assign owners, set due dates, upload files or connect systems. Reminders chase the work so you do not have to.
Pass the audit
Give auditors read-only access, answer requests in one place and close findings without a second evidence hunt.
Frameworks
All the frameworks Indian teams ask for
Six frameworks on one shared control library, with RBI, SEBI and IRDAI guidance alongside for BFSI programmes.
ISO 27001
The global standard for an information security management system (ISMS).
Learn moreISO 27701
Extends ISO 27001 into privacy, and lines up closely with DPDP.
Learn moreSOC 2
Type 1 and Type 2 reports that US buyers ask for.
Learn moreDPDP Act 2023
India's personal data law: notice, consent, rights, breach reporting.
Learn moreISO 9001
Quality management, run together with ISO 27001.
Learn moreISO 42001
An AI management system for companies that build or use AI.
Learn morePlatform
Eight core modules, one shared control library
The same order as Inside AuditIQ and the product menu: compliance frameworks, policy generation, Document Vault, training, CRQ, vendor risk, playbooks and reporting.
Compliance frameworks
Admin completes the Basic Questionnaire; AuditIQ suggests frameworks and Master Admin can assign them manually.
ExploreGenerate policy
Creator drafts from the Policy Questionnaire; Reviewer and Approver workflow with change requests.
ExploreDMS Dashboard
Central view of policies, evidence and certificates in the Document Vault with version history.
ExploreTraining & Assessment
Assign training and assessments; track completion and results across the organisation.
ExploreRisk & Readiness (CRQ)
CRQ, Risk Genome and treatments to quantify risk and plan remediation.
ExploreTPRM
Vendor questionnaires, document collection and approve-or-improve decisions.
ExplorePlaybooks
Guided compliance workflows , module under active development in the product.
ExploreReports & Insights
Board-ready compliance status, gaps, policy progress and assessment summaries.
ExploreThe core idea
Map once, comply six ways
Most controls are the same across frameworks. Access control, incident response and vendor checks show up in DPDP, ISO 27001 and SOC 2 alike.
AuditIQ GRC maps every control to every framework it satisfies. Collect evidence once and it counts everywhere, instead of running six separate projects with six folders of screenshots.
- One control library, pre-mapped across all six frameworks
- Gaps shown per framework, fixed once
- Auditors see only what they need, with read-only access
- Access control and least privilege
- Vendor and third-party risk
- Data retention and deletion
- Incident response and breach notice
controls shared
Integrations
Connect the stack you already use
Evidence should not live in screenshots. Connect cloud, identity, HR, ticketing and DevOps, or import by CSV and API, including on-premises.
Cloud infrastructure
Configuration, logging, encryption and backup evidence from AWS, Azure and GCP.
Identity & access
User lists, MFA status and joiner-mover-leaver evidence for access reviews.
HR & training
Onboarding, background checks and training records for people controls.
Ticketing & ITSM
Change, incident and access-request tickets as evidence, findings pushed back as tasks.
Code & DevOps
Branch protection, code review and deployment evidence for SOC 2 and ISO 27001.
Files, CSV & API
Upload files, import CSVs or push evidence through the API from any internal system.
Industries
Built for how Indian industries get audited
Same platform, different pressure: RBI outsourcing, hospital records, SaaS customer questionnaires, factory ISO programmes.
BFSI
Banks, NBFCs and fintechs that need DPDP with RBI, SEBI or IRDAI expectations in view.
BFSI compliance →Healthcare
Hospitals and health-tech teams handling patient data under DPDP and ISO 27001.
Healthcare →IT & SaaS
Product companies chasing SOC 2 or ISO 27001 to close enterprise deals.
IT & SaaS →Manufacturing
Plants adding ISO 27001 beside ISO 9001 for OEM and export customers.
Manufacturing →Deployment
Deployed your way
Choose where your compliance data lives, without changing how the platform works. Most global GRC tools are cloud-only.
AuditIQ cloud
Fully managed and hosted by AuditIQ. The fastest way to get your first framework live.
- Live in days
- Updates included
- No servers to run
Your cloud
Deployed into your own AWS, Azure or GCP account, under your existing security controls.
- Your cloud account
- Your keys and logs
- Same product
On-premises
Runs entirely inside your data center. Built for BFSI, healthcare and government teams whose data cannot leave the building.
- Air-gap friendly
- Your data center
- Same product
DPDP Rules 2025
Most DPDP obligations apply from 13 May 2027
Consent Manager registration opens on 13 November 2026. Notice, consent, rights, security, breach reporting and Significant Data Fiduciary duties follow on 13 May 2027. Start with a free gap check.
How we compare
Built for Indian rules, not retrofitted
Many global GRC tools started with SOC 2 and added India later. AuditIQ GRC started with India.
DPDP Act 2023, native
DPDP ships as a first-class framework with notice, consent, rights requests, breach reporting and Significant Data Fiduciary duties built in, sharing controls with ISO 27001 and ISO 27701.
- Dates and duties per DPDP Rules 2025
- Reviewed by a practising lawyer
ISO 9001 + ISO 27001
Quality and security run as one integrated management system, with shared audits and corrective actions.
Deployment options
Cloud, your cloud or on-premises. Most GRC tools are cloud-only.
India business hours
A local team that answers in your time zone.
Priced and billed in INR
No USD conversion or surprise FX charges.
AuditIQ vs Scrut · AuditIQ vs Sprinto · AuditIQ vs spreadsheets
Built by practitioners
Built by people who have run audits, not just software
Falgun Rathod, our founder, is the author of A Guide to Cyber Security and Data Privacy, co-author of The Modern SOC and a TEDx speaker on data privacy. AuditIQ GRC is designed around how audits actually run in Indian companies.
Meet the team →Free tools & resources
Start before the sales call
Run the free checks first. Book a demo when you want the platform walkthrough.
GRC ROI calculator
Model hours to evidence one control per year, framework overlap and audit prep, then see rupees and team time saved with shared controls.
Estimate savings → ToolEntity applicability
See which Indian rules and standards typically apply to your entity type.
Check applicability → ToolDPDP applicability check
Seven questions on whether the DPDP Act applies and which duties follow.
Run the check → ToolCompliance readiness score
Score Govern, Operate and Prove for ISO 27001, DPDP, SOC 2 and more.
Get your score →FAQ
Common questions
Is AuditIQ GRC built for the Indian DPDP Act?
Yes. The DPDP Act 2023 is a core framework in AuditIQ GRC, not an add-on. It covers notice and consent, data principal rights, breach reporting and audit evidence, and shares controls with ISO 27001, ISO 27701, ISO 42001, ISO 9001 and SOC 2.
Can AuditIQ GRC run on our own servers?
Yes. You can use AuditIQ cloud, deploy into your own AWS, Azure or GCP account, or run it fully on-premises in your data center. The features are the same in all three.
Do we need separate tools for each framework?
No. All six frameworks run on one shared control library. When you add a framework, AuditIQ GRC shows which controls you already meet and only asks for what is new.
How is AuditIQ GRC different from Scrut or Sprinto?
Scrut and Sprinto are cloud platforms with very large framework libraries (70+ and 200+ respectively, per their websites). The clearest difference is deployment: AuditIQ GRC can also run in your own cloud account or fully on-premises. It is also deliberately focused on six frameworks Indian companies need, with INR pricing. See our Scrut and Sprinto comparisons for dated, sourced details.
How long does it take to get our first framework live?
Most teams have their first framework, controls and policy templates set up in the first week. Getting certified then depends on your scope and your auditor; a first ISO 27001 certification typically takes three to six months.
How much does AuditIQ GRC cost?
Pricing is in Indian rupees and depends on frameworks, entities and deployment. See the pricing page for what drives your quote; you get a written number after a short demo, with no obligation.
Is there a free way to check DPDP readiness first?
Yes. Download the free DPDP compliance checklist or take the 5-minute DPDP readiness check for a scored report.
Make Trust Provable
See AuditIQ GRC run your frameworks
Book a 30-minute live demo. We map DPDP, ISO and SOC 2 onto one control set using your scope, not a slide deck.
- 30 minutes
- No obligation
- DPIIT Registered
- 50% off at launch